

Binance says fake hiring plot fuelled USD $6.3bn theft
Sat, 14th Nov 2026 (Today)
Binance has published an initial account of the US$6.3 billion theft from its wallets. According to the exchange, the attack began months earlier with a compromised software package and a fake recruitment process.
The incident narrative describes a campaign that started in June with a tampered software package and later reached a wallet team engineer through a fictitious employer. Binance said the engineer joined a video call with a fake Chief Executive Officer and downloaded a malicious code repository during the process.
The account adds to growing evidence that attackers are targeting staff with privileged access rather than trying to break cryptographic protections directly. It also points to a wider shift in crypto security, where the operational systems around wallet signing have become a prime target.
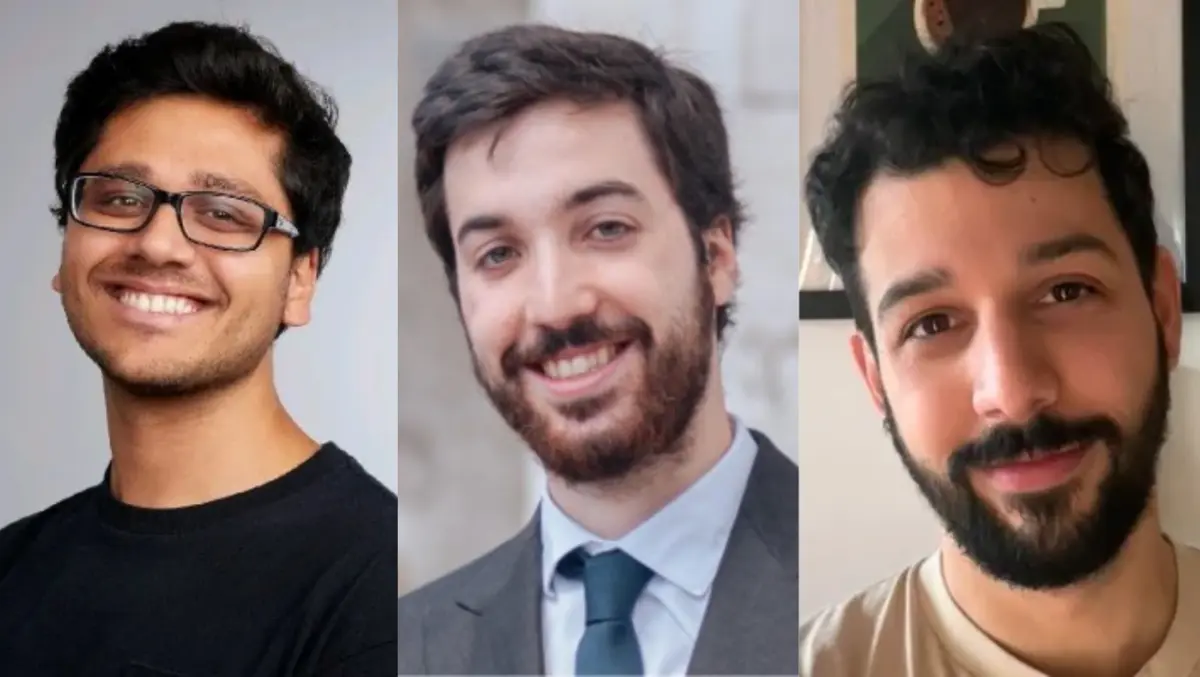
"Binance deserves credit for publishing a detailed timeline this quickly. The key moment came in Sep, when an engineer met on video with the CEO of a company that didn't exist, trusted what he saw and ran the code he was given. Everything technical that followed depended on that one conversation going the attacker's way. When Binance caught a tampered AI tool in Jun, it replaced the device and changed credentials, but new credentials couldn't erase what the attacker had already learned about who was on the wallet team. Once attackers know who holds the keys, they often go after those people directly, and a recruiter's pitch is one of the few approaches a target is likely to welcome without suspicion.
Expect more fake hiring processes aimed at engineers with privileged access, complete with fake executives on video calls. Security teams should treat recruiting outreach to those engineers as part of the attack surface and keep interview code off any machine near production. They should also confirm who's on the other end of a video call before anyone acts on what was said. Binance says it's increasing its investment in AI-enabled detection, and that detection has to run during the live conversation, before anything gets downloaded," said Rohan Gupta, Chief Executive Officer and Co-founder of Diopter.
Attack path
Security specialists said the details fit a pattern seen in other major crypto thefts. Rather than stealing private keys outright, attackers appear to have targeted the systems and workflows that can authorise transactions.
"Crypto has made it very hard to steal the keys that move funds, so attackers now go after the people and the software around those keys that sign transactions. In this case, it seems the attacker compromised Binance's signing system so that it would send malicious withdrawals. Bybit followed the same pattern last year, and Bitget did in September," said Gonçalo Magalhães, Head of Security at Immunefi.
"Other researchers echoed that interpretation, focusing on the simplicity of the on-chain element compared with the effort required to reach internal systems with high levels of privilege. The implication is that controls around staff devices, software packages, interviews and approval chains now sit much closer to the centre of exchange security.
"One of the striking things about this breach is how little code was actually needed on-chain. The sweeper contract was only around 130 lines. That is a useful reminder that the sophistication of an attack is not always in the smart contract itself. The hard part is sometimes getting access to a system powerful enough to make very simple code devastating.
"The key issue here is how the attackers were able to gain access to infrastructure with enough privilege to authorise withdrawals across multiple blockchains.
"In crypto, we naturally focus heavily on protecting private keys and auditing smart contracts. But the people, infrastructure and workflows capable of instructing those keys are part of the security perimeter too. If an attacker compromises that operational layer, they may not need to steal a key or discover an exotic smart-contract vulnerability at all.
That is what makes this incident particularly interesting: the on-chain execution appears relatively simple, while the real sophistication was in reaching the privileged systems behind it. The broader lesson is that access controls, internal infrastructure and transaction-authorisation processes need to be secured with the same intensity as the keys themselves," said Simone Imbrescia, VP of Engineering, Product and Design at Immunefi.
Broader Risks
Threat intelligence analysts said the Binance case also underlines the enduring role of malware and credential theft in large breaches. A single infected device can expose passwords, sessions and internal knowledge that attackers later use across several stages of an intrusion.
"A US$6.3 billion attack that started with a malware download shows how a single compromised device can open the door to a devastating breach," said Borja Rodriguez, Head of Threat Intelligence at Outpost24.
"Attackers don't need to break through every layer of security if they can steal their way in. Our latest research found infostealer-sourced credentials linked to 72% of organizations analyzed. And a stolen password may be just the beginning. Malware can also expose session cookies and other sensitive data, giving attackers multiple ways in. Continuous monitoring for exposed credentials is critical to catching these warning signs early, before attackers turn a single infection into a much larger compromise. But detection alone isn't enough. Security teams must investigate what else was stolen and shut down every potential route back in," Rodriguez added.