Australian Signals Directorate stories
Ageing technology is leaving critical services exposed as AI lets attackers exploit known weaknesses at machine speed, experts say.
Australian firms could face faster breaches as model-driven attackers shrink exploit times to hours, making containment and zero trust vital.
Australian firms could be losing value and facing security risks as idle decommissioned devices wipe away recovery value and add labour costs.
Boards and regulators are being urged to prove critical services can hold up as frontier AI speeds attacks and shortens response times.
Most organisations in Australia and New Zealand still cannot match machine-speed attacks, leaving blind spots and manual defences exposed.
The flaws could have let attackers hijack identities and take over domains in environments where Active Directory still runs most enterprise access.
Shorter certificate lifespans are forcing Australian and New Zealand businesses to automate renewals or risk outages and security gaps.
Security teams are drowning in AI-generated bug reports, and 11 early users are already testing a system that filters the noise.
Continuous validation is being pushed as boards and insurers seek proof that ageing-system cyber controls still work as threat windows shrink.
Staff could soon lose access to Wi-Fi, VPNs and APIs as public certificate authorities stop issuing login certificates and the free ones expire in October.
Australian businesses face faster, cheaper attacks as the ASD urges tighter control of privileged access and AI identities.
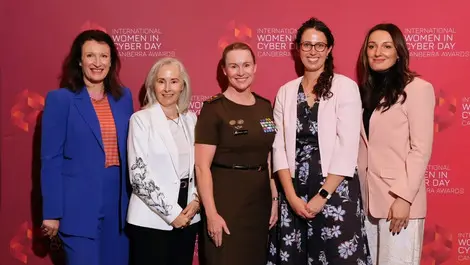
Skills shortages in Canberra's cyber sector are being tackled through awards for women, mentors and employers boosting inclusion.
Australian firms are leaving staff and contractors with excessive access, making insider incidents harder to spot, report and contain.
Local hosting in Sydney eases compliance worries for Australian firms using AI tools that may expose prompts, code and credentials.
Australian agencies can now assess JFrog faster, after the platform cleared a PROTECTED-level IRAP review for security approvals.
Disconnected vulnerability data is leaving Australian organisations unable to judge which weaknesses threaten critical services, compliance, or customers.
Manufacturers supplying banks and other regulated firms face tougher contract demands on resilience, cyber risk and continuity as CPS 230 beds in.
Most Australian organisations still rely on manual processes, leaving them exposed to AI-automated cyber attacks, according to an Elastic survey.
Australians lost AUD $166.8 million to payment redirection scams in 2025, as finance teams struggled to verify supplier bank-detail changes.
Australian agencies could now buy Quest's security and data platforms without repeating lengthy internal reviews, after independent PROTECTED-level assessment.